Healthcare Compliance

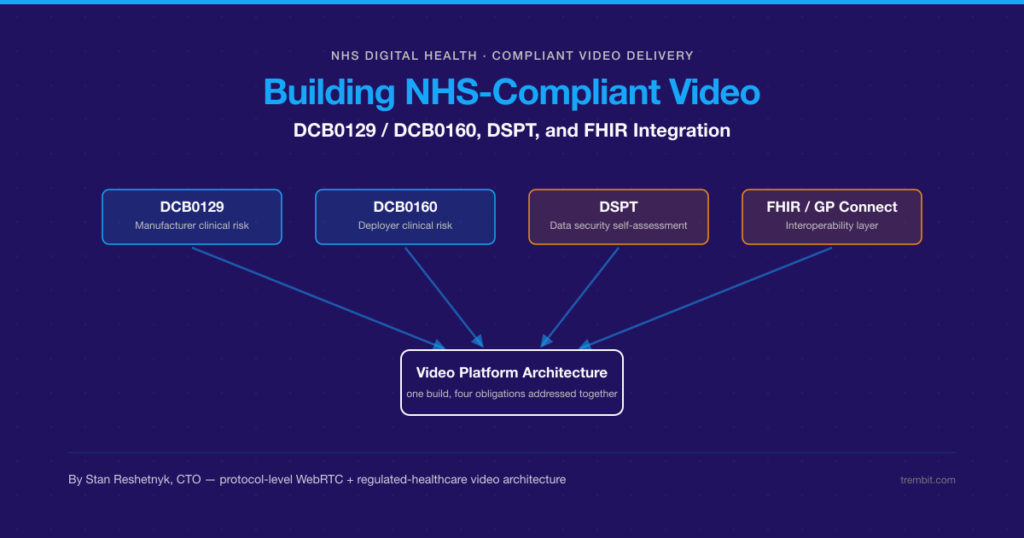
Building NHS-Compliant Video: DCB0129/DCB0160, DSPT, and FHIR Integration

Building NHS-Compliant Video: DCB0129/DCB0160, DSPT, and FHIR Integration

An NHS-facing video or telemedicine platform has to satisfy at least four distinct obligations that a generic consumer video app never touches. DCB0129 governs clinical risk management for the manufacturer who builds the system. DCB0160 governs clinical risk management for the deploying NHS organisation putting it into live clinical use. The DSPT (Data Security and Protection Toolkit) is the NHS’s annual data-security self-assessment. And FHIR / […]

WebRTC in Telemedicine: When HIPAA Requirements Conflict With Video Performance

WebRTC in Telemedicine: When HIPAA Requirements Conflict With Video Performance

The promise of telemedicine is simple: deliver healthcare anywhere, at any time, with the same quality as an in-person visit. However, achieving this promise creates a fundamental tension between two critical requirements — HIPAA compliance and video performance. Healthcare organizations must simultaneously protect patient privacy through rigorous security measures while delivering the low-latency, high-quality video […]

Is Your Telehealth Platform Actually HIPAA Audit Ready?

Is Your Telehealth Platform Actually HIPAA Audit Ready?

“We’re HIPAA compliant.” Every telehealth platform says it. Investors hear it. Customers read it on landing pages. Regulators hear it right before they start asking questions nobody can answer. The telehealth market has exploded — and so has compliance theater. By 2026, the difference between HIPAA audit ready telehealth platforms and those merely claiming compliance […]

How to Implement HIPAA Compliant AI Integration

How to Implement HIPAA Compliant AI Integration

The telehealth industry faces a critical challenge: artificial intelligence promises transformative capabilities in clinical documentation, patient triage, and predictive analytics, yet HIPAA regulations weren’t designed with large language models in mind. With fines reaching $1.5 million per violation category annually, the stakes are existential. Healthcare organizations watch competitors announce AI features while their own legal […]

Telehealth Patient Intake Security: What CTOs Must Get Right

Telehealth Patient Intake Security: What CTOs Must Get Right

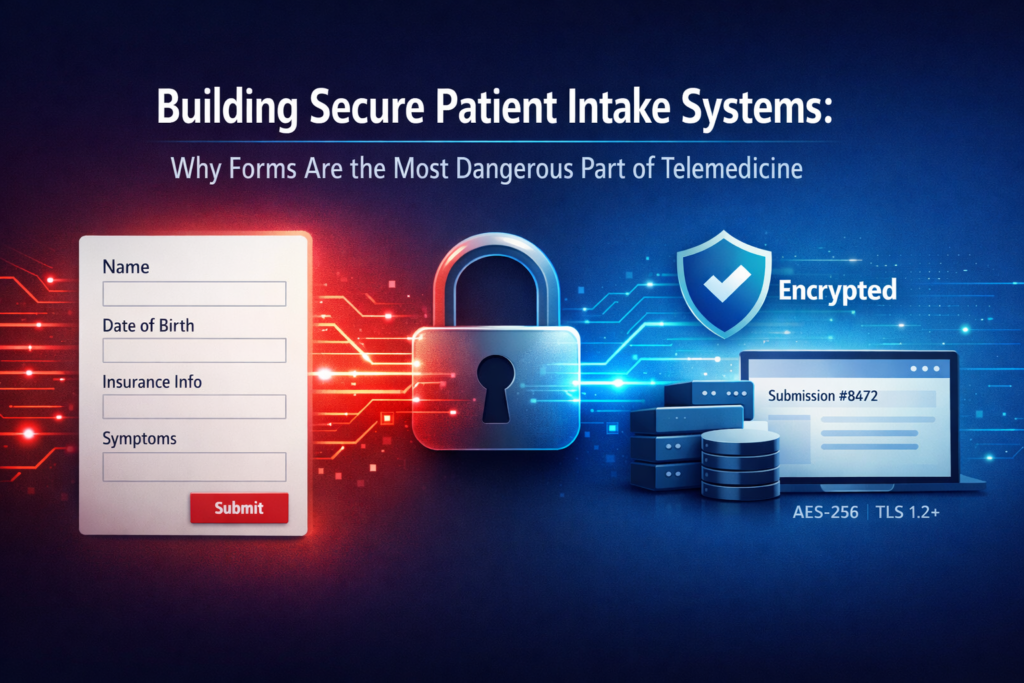
Patient intake forms seem mundane. They’re the unglamorous paperwork of healthcare — medical histories, insurance information, symptom descriptions. Yet telehealth patient intake security represents one of the highest-risk challenges in any modern healthcare platform — far more consequential than its paperwork appearance suggests. Consider what happens during typical patient intake: individuals provide comprehensive personal information, […]

Healthcare Compliance Readiness: A Guide for Telehealth Startups

Healthcare Compliance Readiness: A Guide for Telehealth Startups

Funding rounds and enterprise sales contracts share a common inflection point: the moment a potential investor or customer asks for your security documentation. For telehealth startups, this moment arrives earlier than most founders expect and reveals more than most engineering teams are prepared for. Compliance audits and enterprise due diligence aren’t just bureaucratic exercises. They’re […]

How to Meet KBV Certification Requirements for Video Consultations

How to Meet KBV Certification Requirements for Video Consultations

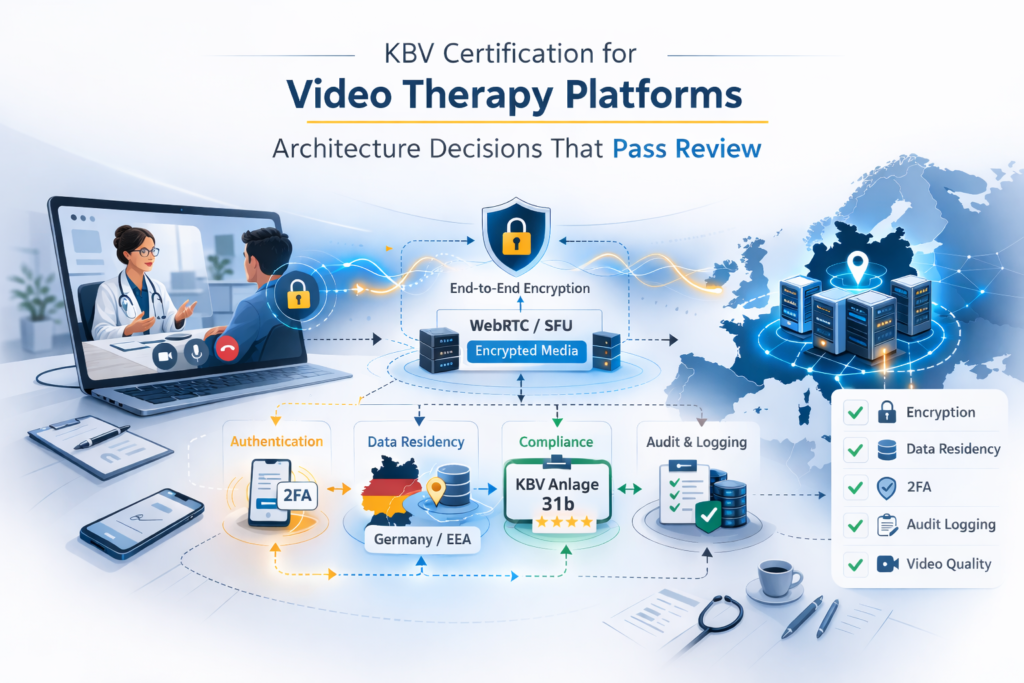
If you’re building a video therapy platform for the German market, KBV certification isn’t a checkbox at the end of your roadmap. It’s a constraint that shapes every major architecture decision from day one — and teams that treat it otherwise tend to find out the hard way, usually six months into development and weeks […]

How to Design GDPR-Compliant Healthcare Video Architecture

How to Design GDPR-Compliant Healthcare Video Architecture

GDPR compliance in healthcare video is one of those problems that looks manageable from a distance and reveals its depth only once you’re inside it. A general understanding of data protection principles — consent, minimization, right to erasure — doesn’t translate directly into architecture decisions. The question isn’t whether you understand GDPR. It’s whether your […]

How to Design Role-Based Access for Healthcare Platforms

How to Design Role-Based Access for Healthcare Platforms

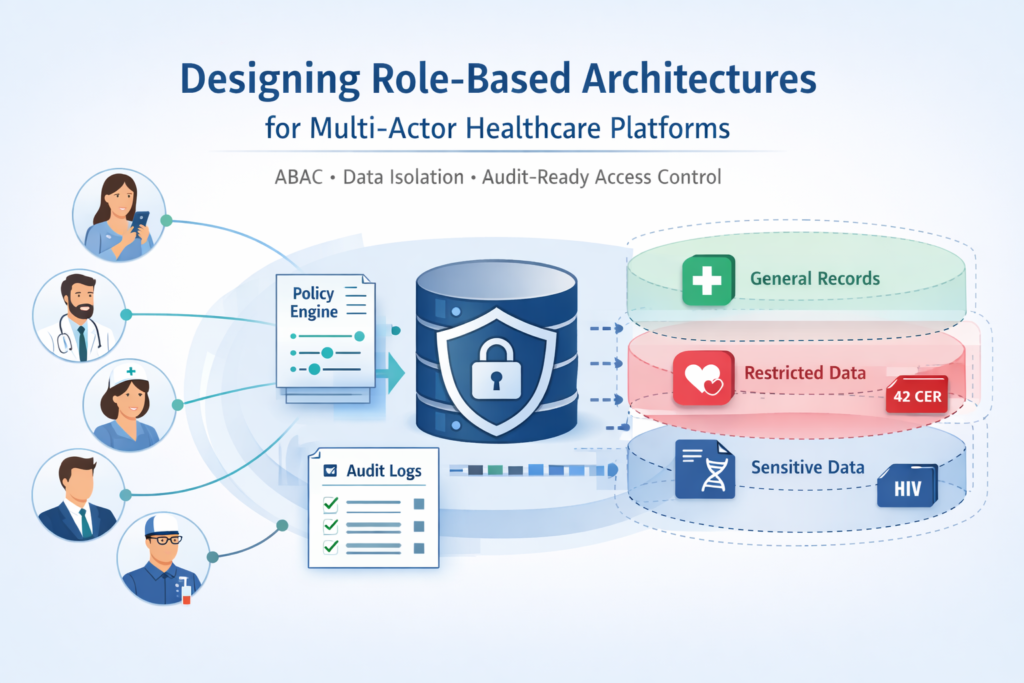
Healthcare platforms operate in a uniquely complex permission landscape. A single patient record might be accessed by the patient themselves, their primary care physician, a consulting specialist, a nurse coordinator, billing staff, quality assurance reviewers, external lab technicians, insurance verifiers, and platform administrators — each with legitimate but dramatically different access needs. Traditional role-based access […]

HIPAA-Grade Telehealth: From MVP to Audit-Ready – 2026

HIPAA-Grade Telehealth: From MVP to Audit-Ready – 2026

Many platforms claim ‘HIPAA-compliant.’ Very few are audit-ready. The telehealth market has exploded. By 2026, platforms face a fundamental credibility problem: everyone claims HIPAA compliance, but when regulators come knocking, or breaches occur, the difference between documentation theater and audit-ready infrastructure becomes brutally apparent. A checkbox on a security questionnaire and genuine regulatory readiness are […]

Telehealth Security Compliance: HIPAA, GDPR & PIPEDA

Telehealth Security Compliance: HIPAA, GDPR & PIPEDA

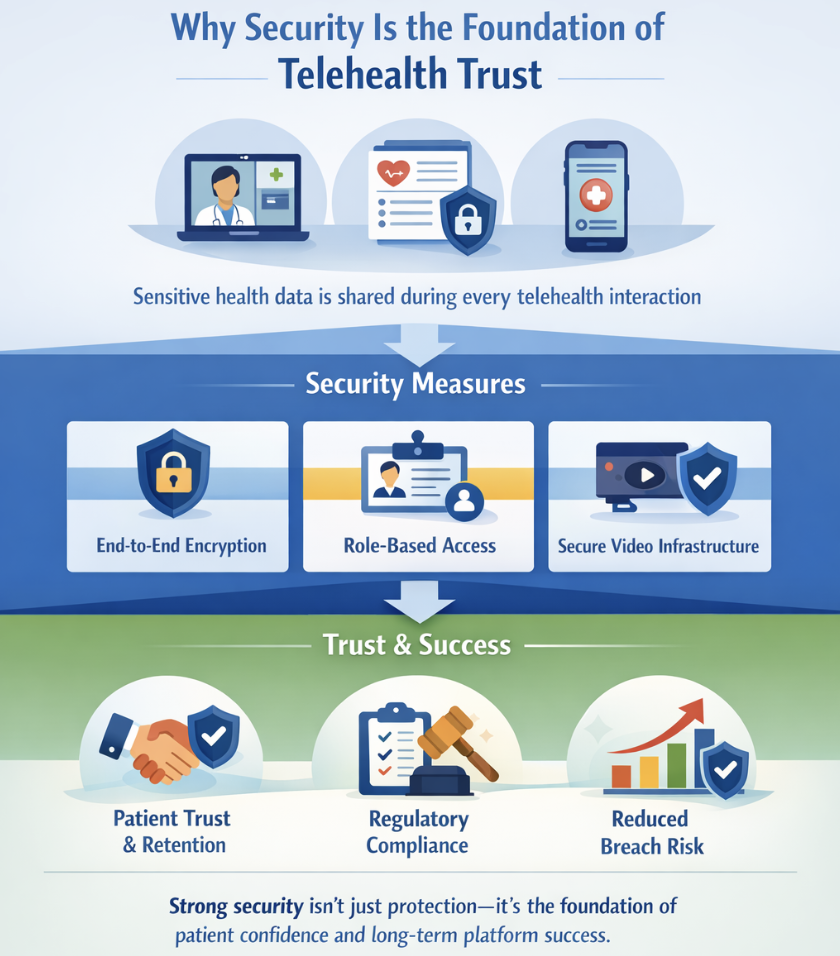
Telehealth has moved from a “nice-to-have” innovation to a core component of modern healthcare delivery. Patients now expect remote consultations, secure video calls, and seamless access to their medical data — without compromising privacy or safety. For healthcare providers and digital health startups, this creates a critical challenge: how to scale telehealth solutions while maintaining […]

Designing HIPAA-Compliant Telemedicine Architectures: A Technical Blueprint for 2026

Designing HIPAA-Compliant Telemedicine Architectures: A Technical Blueprint for 2026

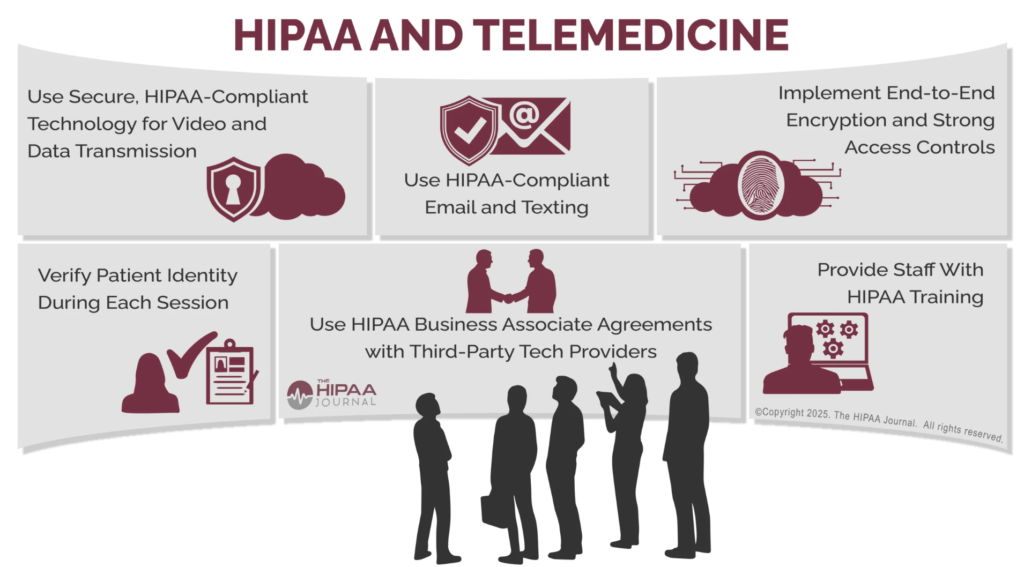
As telemedicine redefines healthcare delivery in 2026, it is critical to design architectures that are HIPAA-compliant from the start, safeguarding patient data against new cyber threats and regulatory pressures. For CTOs, compliance is a top concern due to severe financial, legal, and reputational risks, making it imperative to build correctly at the outset. Trembit specializes […]

Building HIPAA-Compliant Video Consultations with WebRTC and LiveKit

Building HIPAA-Compliant Video Consultations with WebRTC and LiveKit

To build HIPAA-compliant video consultations with WebRTC and LiveKit: encrypt media in transit with DTLS-SRTP and at rest with AES-256, enforce MFA and role-based access control, sign a Business Associate Agreement (BAA) with every vendor that touches PHI, and keep immutable audit logs of access. WebRTC mandates transport encryption; HIPAA compliance comes from how you […]

KBV-Listed Telehealth Developers in Germany: 2026 Guide

KBV-Listed Telehealth Developers in Germany: 2026 Guide

In Germany, a practice can bill a video consultation to statutory insurance only if it uses a video service on the official KBV list of certified providers (Anlage 31b BMV-Ä). People often call these services “KBV-certified”. Strictly, KBV says they are certified by independent certification bodies under KBV and GKV-Spitzenverband rules. This guide covers 20 […]

Navigating Telemedicine Regulations in Europe: A Practical Guide for App Developers

Navigating Telemedicine Regulations in Europe: A Practical Guide for App Developers

As digital healthcare accelerates across Europe, developers building telemedicine platforms – especially mobile and web applications – face the challenge of navigating a growing landscape of regulations. Crafting a compliant healthcare app goes beyond ticking legal boxes; it requires building trust, security, and usability into your product from the outset. This guide unpacks the current […]